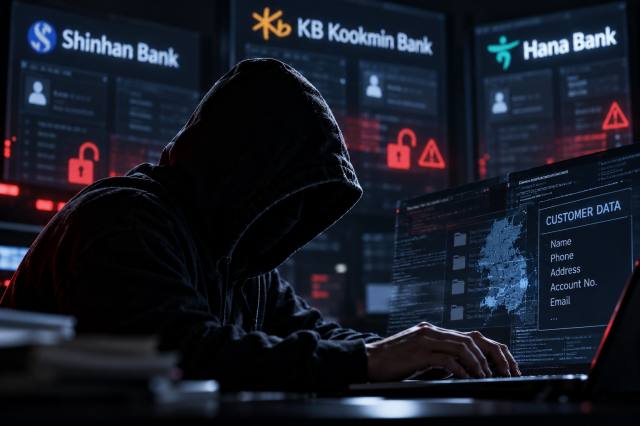
SEOUL, October 05 (AJP) - A wave of cyberattacks on South Korean banks has exposed a weak point outside their heavily protected core banking networks, with hackers targeting employee and sales-support systems that still contain sensitive customer data.
Recent breaches at Shinhan Bank, KB Kookmin Bank and Hana Bank did not penetrate their main internet or mobile banking systems. Instead, attackers accessed peripheral services used by loan recruiters, employees and sales staff.
At Shinhan, attackers bypassed authentication on a simplified inquiry service for loan recruiters, exposing information belonging to about 25,000 customers.
The breach is notable because Shinhan had already reviewed authentication-bypass vulnerabilities in 2024 following a request from the Financial Supervisory Service and reported taking corrective measures, according to its information-security disclosure.
Similar weaknesses appeared elsewhere. KB Kookmin was breached through an employee mobile support system, while attackers accessed Hana through an outside sales support system. Neither involved the banks' core transaction networks.
The incidents are raising questions over whether banks' cybersecurity defenses extend consistently beyond their most heavily protected systems.
South Korea's major banks spend tens of billions of won annually on information security. Last year, KB Kookmin spent 43.3 billion won ($30 million), followed by Hana with 37.2 billion won, Shinhan with 36.9 billion won and Woori with 36.4 billion won.
Financial authorities have identified insufficient authentication, access controls and unaddressed vulnerabilities among the weaknesses exposed by the recent attacks. Financial Services Commission Chairman Lee Eog-weon warned that even a single unmanaged gap could undermine an otherwise robust security system.
The attacks suggest that protecting core banking networks alone may no longer be enough, as hackers increasingly search for weaker systems connected to financial institutions.
Copyright ⓒ Aju Press All rights reserved.