Daishin Securities said Wednesday that personal and credit information belonging to 38,490 customers had been leaked. Mirae Asset Asset Management was also reported to have suffered a hacking incident, with authorities assessing the situation, while cryptocurrency exchange Bithumb acknowledged a breach of its internal mobile system that exposed personal information.
The cases add to a wave of breaches across banks, savings banks and other financial businesses. The Financial Services Commission said on Oct. 14 that cyber incidents had been identified at 16 firms, with roughly 100,000 records exposed. That was an interim tally before the latest disclosures, and investigators were still examining whether the attacks were connected.
Daishin said it first detected signs of unauthorized access on Oct. 17 to a server supporting remote securities-account opening for discretionary investment services. It blocked the internet addresses used in the attack, including those used to bypass access restrictions, and notified regulators.
Working with the Financial Security Institute, the brokerage reviewed about 60,000 requests disguised as legitimate service traffic over a 10-day investigation. It confirmed the information leak on Oct. 26.
Eight categories of information were exposed: customer names, email addresses, postal addresses, communications IDs, bank names, bank account numbers, Daishin securities account numbers and mobile phone numbers.
The bank and securities account numbers and mobile phone numbers were encrypted, the company said.
Daishin said it had found no evidence so far of secondary harm or unauthorized access to its core business systems. It began notifying affected customers individually on Wednesday and pledged compensation under applicable laws and procedures for losses caused by the breach.
The brokerage also promised tighter access controls, stronger detection and blocking of suspicious activity, and security checks on systems connected to outside services.
“We take this leak of personal and credit information very seriously and deeply apologize to our customers,” Chief Executive Jin Seung-wook said. “We will responsibly carry out the measures necessary to protect customers and prevent a recurrence.”
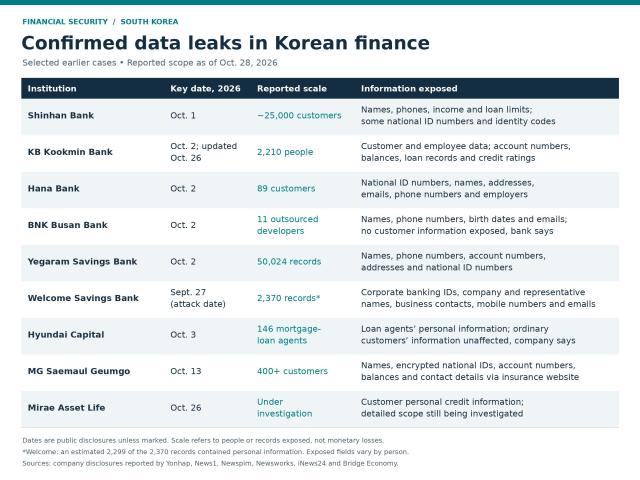
Earlier cases are also proving more extensive than initially reported.
A further review identified 2,091 additional people, including 1,631 customers and 460 current or former employees. Exposed information included account numbers, deposit balances, loan records and credit ratings, although the information varied by individual. The bank said the revision reflected further findings from the original incident.
Separately, Mirae Asset Life Insurance confirmed a customer credit-information leak on Oct. 26 after detecting suspicious activity the previous day. The incident affected parts of its insurance application system and website. The number of affected customers and the precise information exposed remained under investigation.
The widening disclosures come despite repeated security checks. An industrywide review of 555 firms found shortcomings at 130, including missing security updates, inadequate monitoring and weaknesses in authentication and access controls, the FSC said. Authorities are pursuing broader inspections and stronger accountability for senior management.
Copyright ⓒ Aju Press All rights reserved.