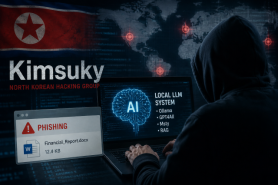
SEOUL, November 16 (AJP) - Suspected North Korean hackers impersonated a South Korean parliamentary aide to target participants in a National Assembly seminar, cybersecurity firm Genians said Monday. The attackers used payment paperwork as bait and deployed newly identified malware capable of stealing files and remotely monitoring infected computers.
The emails targeted an attendee of a September seminar, initially omitting an attachment. When the recipient requested the missing document, the attackers sent a malicious archive containing a shortcut disguised as a Hangul document. Opening it triggered hidden commands that downloaded malicious scripts while displaying a payment application form to avoid suspicion.
The attackers used an online note-sharing service to deliver and update commands, later deploying malware that Genians named NodeLinkRAT. The firm linked the campaign to North Korea-associated hacking group Kimsuky with moderate confidence, citing overlaps with previous operations, but cautioned that another group could have copied the techniques.
Tags: North Korea, Pyongyang, Kimsuky, cyberattack, cybersecurity
The emails targeted an attendee of a September seminar, initially omitting an attachment. When the recipient requested the missing document, the attackers sent a malicious archive containing a shortcut disguised as a Hangul document. Opening it triggered hidden commands that downloaded malicious scripts while displaying a payment application form to avoid suspicion.
The attackers used an online note-sharing service to deliver and update commands, later deploying malware that Genians named NodeLinkRAT. The firm linked the campaign to North Korea-associated hacking group Kimsuky with moderate confidence, citing overlaps with previous operations, but cautioned that another group could have copied the techniques.
Tags: North Korea, Pyongyang, Kimsuky, cyberattack, cybersecurity
Lee Jung-woo
I studied philosophy in college, and sociology and journalism in graduate school. I cover North Korea, South Korean politics, foreign affairs and films. I enjoy Nordic cinema, Indian cuisine and Japanese detective novels. I have a cat and like bright, acidic coffee.
Copyright ⓒ Aju Press All rights reserved.