SEOUL, November 12 (AJP) - South Korea’s financial industry reported 40 cyber incidents in just over a month, exposing about 473,000 personal data records and resulting in roughly 1 billion won in stolen funds, underscoring the scale and speed of hacking facilitated by AI tools.
As hackers employ AI technologies to find weaknesses and turn them into attacks, financial companies face a shrinking window to respond.
The incidents affected 37 financial companies between Sept. 30 and Nov. 3, according to the Financial Services Commission (FSC). Banks, insurers, securities firms and digital financial service providers were among those hit.
The stolen funds came from company-managed accounts, including cryptocurrency wallets and accounts holding customer deposits. No losses to individual customers had materialized as of the regulator’s Nov. 5 announcement.
The incidents have not all been attributed to AI. But a separate investigation by U.S. cybersecurity firm CrowdStrike showed that attackers were already using the technology against Korean financial institutions.
In an Oct. 7 report, CrowdStrike identified a campaign that used ARTEX, an AI-powered security testing tool, alongside large language models to target Korean financial organizations. Active from late September to early October, the campaign resulted in data theft, the company said.
AI can help attackers search for software weaknesses and develop ways to exploit them, potentially moving faster than companies can investigate and install fixes.
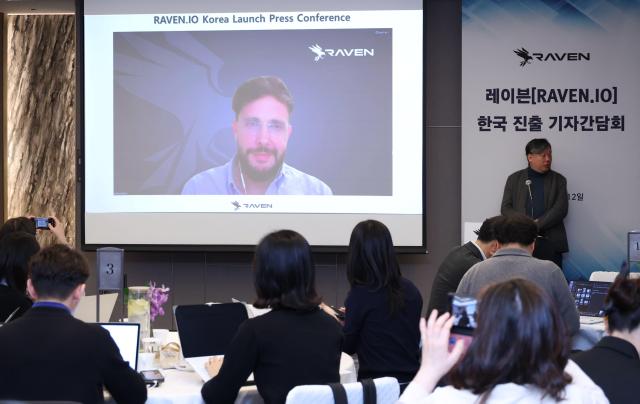
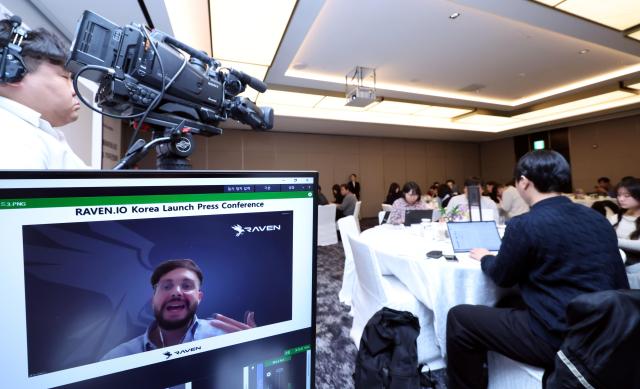
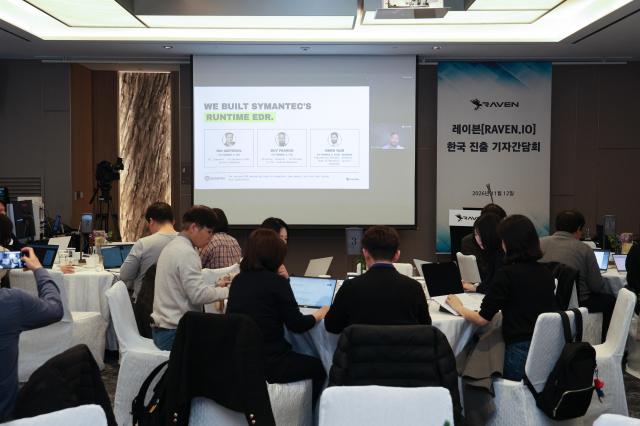
“It is so easy to find the vulnerability and build an exploit today using AI,” said Roi Abitboul, co-founder and CEO of cybersecurity company Raven.io, during a press briefing in Seoul on Thursday.
Abitboul, who joined remotely, said AI was narrowing the time between discovering a software flaw and using it to launch an attack.
That shrinking interval is central to Raven’s pitch as it enters South Korea, with banks and insurance companies among its initial targets.
Modern financial systems rely on software assembled from many components. Banks write some themselves and obtain others from outside developers, including publicly available code known as open-source libraries.
These libraries help developers build applications faster and at lower cost. Their openness also allows security researchers and attackers to study the same code for weaknesses.
Installing security updates remains an essential defense. The difficulty arises when attackers exploit a weakness before a fix is available — or before a company has deployed it.
Raven says its technology is designed to help protect applications during that gap by monitoring what individual software components do while they are running.
Abitboul compared the approach to “having a camera on every library.”
The company installs a monitoring program, known as an agent, on the server running an organization’s applications. The agent observes which libraries are being used, what they do and how they interact with the rest of the system.
Raven says it uses its understanding of those components to identify actions outside their intended functions. A component designed to process data, for example, might trigger a warning if it unexpectedly tries to launch an unrelated program or access a sensitive file.
The company says its system can block such an action without shutting down the entire application — a distinction that matters for banks, where an interruption could disrupt payments or other customer services.
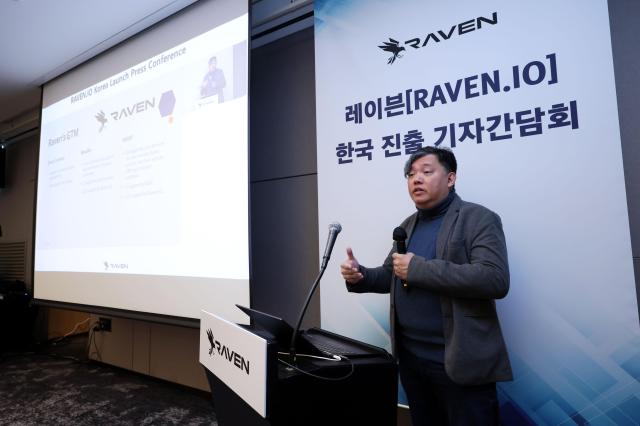
“We don’t change your source code. We don’t kill your application,” said Adrian Ong, managing director of The Executive Action, Raven’s Singapore-based partner overseeing its Korean expansion.
Raven also says its protection does not depend on a flaw first receiving an official vulnerability identifier, known as a CVE, or on a developer releasing an update.
“The moment you deviate from it, we catch you,” Abitboul said, referring to behavior outside a component’s expected function.
The proposition is straightforward: restrict what software is allowed to do, regardless of whether a human attacker or an AI tool is trying to misuse it.
Delivering that protection without disrupting legitimate activity is more complicated. Unusual software behavior is not always malicious, and incorrectly blocking it could itself interfere with a financial service.
Abitboul said Raven’s technology uses approximately 0.2 percent of a server’s processing capacity and 200 to 300 megabytes of memory. Those performance figures have not been independently verified, and the company has not demonstrated that its product would have prevented the recent Korean attacks.
Founded in 2023 by Abitboul and two longtime colleagues who previously developed security technology at Javelin Networks and Symantec, Raven is entering Korea as regulators intensify scrutiny of financial companies’ defenses.
The FSC announced on Nov. 5 that it would inspect approximately 580 financial businesses, strengthen vulnerability assessments and examine internal security controls following the series of incidents.
Abitboul said the attacks were a major reason Raven had prioritized South Korea despite its smaller market compared with the United States.
“This market is very sophisticated,” he said, explaining that the urgency created by the breaches had strengthened the case for expansion.
The company says it already serves customers in the United States, Western Europe and Africa. In Korea, it plans to pursue direct contracts and work with local resellers and companies that manage cybersecurity for other businesses.
Several Korean organizations are testing the technology to assess its effectiveness and business value, Ong said. He declined to identify them, citing confidentiality agreements. No completed Korean commercial contracts were confirmed at the briefing.
Ong, who first worked in South Korea’s cybersecurity industry in 2006, said the biggest change he had witnessed was the speed at which attacks could now develop.
For financial companies, the challenge is to investigate weaknesses, deploy defenses and keep essential services running before an attacker finds a way through.
“You can have many things, smart people, AI, whatever, money, but you never have enough time,” Ong said.
Copyright ⓒ Aju Press All rights reserved.